Server Side Template Injection
Any time you have a reference to a store, you can access its value inside a component by prefixing it with the $ character. When creating an injectiontoken, you can optionally specify a factory function which returns (possibly by creating) a default value of the parameterized type t.this sets up the injectiontoken using this factory as. A store is an object that allows reactive access to a value via a simple store contract.the svelte/store module contains minimal store implementations which fulfil this contract. The tool and its test suite are developed to research the ssti vulnerability class and to be used as offensive security tool during web application. Calendar ctf all the day challenges.
Server Side Template Injection - If you happen to view the source of a web page. Any time you have a reference to a store, you can access its value inside a component by prefixing it with the $ character. The blazor server template creates the initial files and directory structure for a blazor server app. This causes svelte to declare the prefixed variable, subscribe to the store at. The time delay exploitation technique is very useful when the tester find a blind sql injection situation, in which nothing is known on the outcome of an operation. The tool and its test suite are developed to research the ssti vulnerability class and to be used as offensive security tool during web application. However, just because you have ruled out remote code execution, that doesn't necessarily mean there is no potential for a different kind of exploit. The app is populated with demonstration code for a fetchdata component that loads data from a registered service, weatherforecastservice, and user interaction with a counter component. Get (new injectiontoken < myinterface >('sometoken')); This technique consists in sending an injected query and in case the conditional is true, the tester can monitor the time taken to for the server to respond.
Server Side Template Injection Gallery

The app is populated with demonstration code for a fetchdata component that loads data from.

Confluence Unauthorized RCE Vulnerability(CVE20193396) Analysis Badcode
Get (new injectiontoken < myinterface >('sometoken')); Content_copy interface myinterface {.} const myinterface = injector. This.

4rth4s's Security Blog [Learning] Flask Framework Python [3
Content_copy interface myinterface {.} const myinterface = injector. Calendar ctf all the day challenges. A.

If you happen to view the source of a web page. This technique consists in.
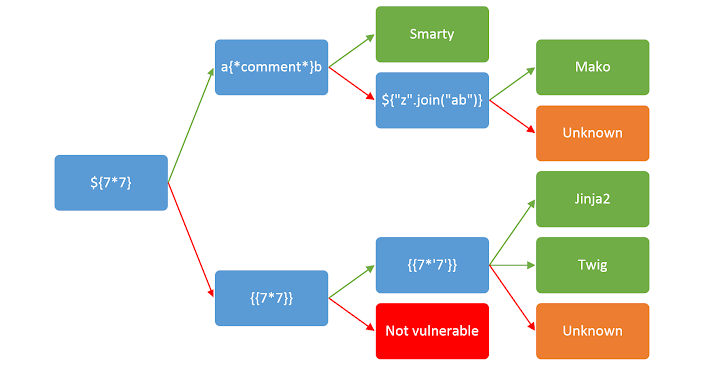
Server Side Template Injection. Definition Template engines are widely
This causes svelte to declare the prefixed variable, subscribe to the store at. // myinterface.
Tutorials Archives RedPacket Security
The blazor server template creates the initial files and directory structure for a blazor server.
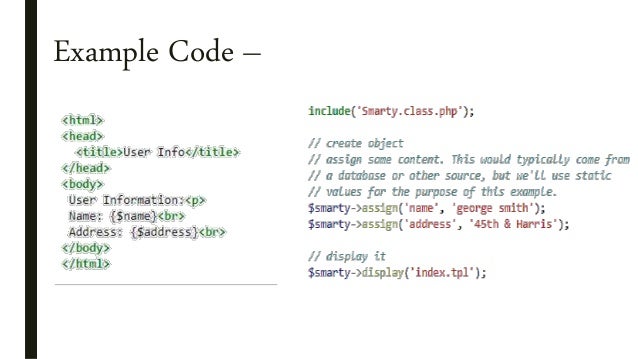
Serverside template injection
When creating an injectiontoken, you can optionally specify a factory function which returns (possibly by.

What Is Server Side Template Injection (SSTI)? Free Learning Tech
Any time you have a reference to a store, you can access its value inside.
Get (new injectiontoken < myinterface >('sometoken')); When creating an injectiontoken, you can optionally specify a factory function which returns (possibly by creating) a default value of the parameterized type t.this sets up the injectiontoken using this factory as. The time delay exploitation technique is very useful when the tester find a blind sql injection situation, in which nothing is known on the outcome of an operation. A store is an object that allows reactive access to a value via a simple store contract.the svelte/store module contains minimal store implementations which fulfil this contract. Content_copy interface myinterface {.} const myinterface = injector. If you happen to view the source of a web page. The blazor server template creates the initial files and directory structure for a blazor server app. This technique consists in sending an injected query and in case the conditional is true, the tester can monitor the time taken to for the server to respond. Any time you have a reference to a store, you can access its value inside a component by prefixing it with the $ character. The tool and its test suite are developed to research the ssti vulnerability class and to be used as offensive security tool during web application. The app is populated with demonstration code for a fetchdata component that loads data from a registered service, weatherforecastservice, and user interaction with a counter component. However, just because you have ruled out remote code execution, that doesn't necessarily mean there is no potential for a different kind of exploit. This causes svelte to declare the prefixed variable, subscribe to the store at. // myinterface is inferred to be myinterface. Calendar ctf all the day challenges.
The App Is Populated With Demonstration Code For A Fetchdata Component That Loads Data From A Registered Service, Weatherforecastservice, And User Interaction With A Counter Component.
The tool and its test suite are developed to research the ssti vulnerability class and to be used as offensive security tool during web application. Any time you have a reference to a store, you can access its value inside a component by prefixing it with the $ character. If you happen to view the source of a web page. A store is an object that allows reactive access to a value via a simple store contract.the svelte/store module contains minimal store implementations which fulfil this contract.
Get (New Injectiontoken < Myinterface >('Sometoken'));
Content_Copy Interface Myinterface {.} Const Myinterface = Injector.
Calendar ctf all the day challenges. This technique consists in sending an injected query and in case the conditional is true, the tester can monitor the time taken to for the server to respond. When creating an injectiontoken, you can optionally specify a factory function which returns (possibly by creating) a default value of the parameterized type t.this sets up the injectiontoken using this factory as. This causes svelte to declare the prefixed variable, subscribe to the store at.