Nist 800-171 Access Control Policy Template
Cmvp validation authority updates to iso/iec 24759 and. February 2020 (includes updates as of january 28, 2021) supersedes: The fundamental principles (tenets) of information security are confidentiality, integrity, and availability. Every element of an information security program (and every security control put in place by an entity) should be designed to achieve one or more of these principles. As components of the template, not the policy.
Nist 800-171 Access Control Policy Template - The fundamental principles (tenets) of information security are confidentiality, integrity, and availability. With aws, you control where your data is stored, who can access it, and what resources your organization is consuming at any given moment. As components of the template, not the policy. Cmvp validation authority updates to iso/iec 24759 and. The exception is the parameters property that passes values from the policy to the template. Extensible access control markup language (xacml) and next generation access control (ngac). Every element of an information security program (and every security control put in place by an entity) should be designed to achieve one or more of these principles. A comparison of attribute based access control (abac) standards for data service applications: Together, they are called the cia triad. February 2020 (includes updates as of january 28, 2021) supersedes:
Nist 800-171 Access Control Policy Template Gallery
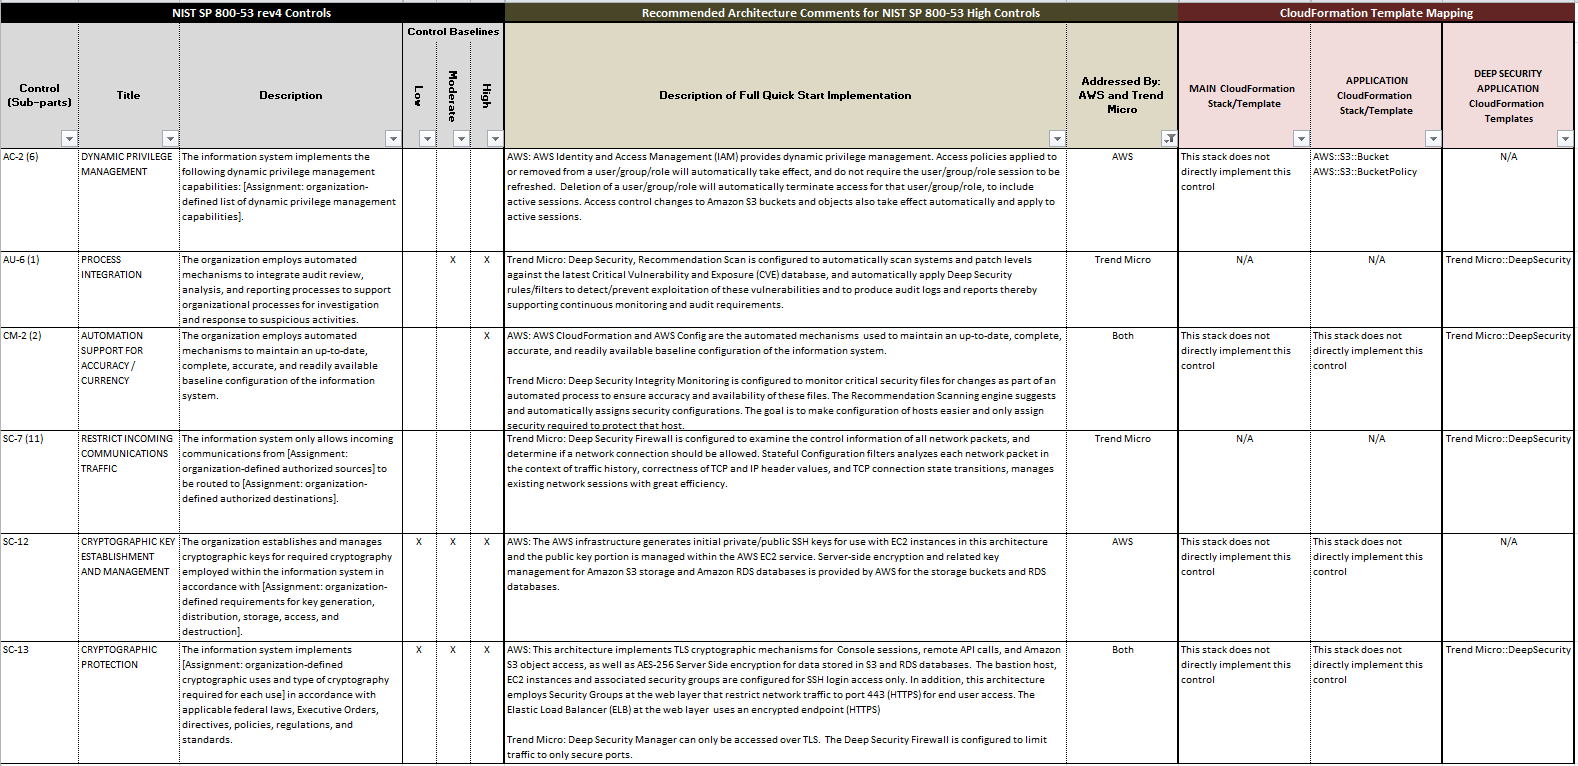
Nist Policy Templates
The exception is the parameters property that passes values from the policy to the template..
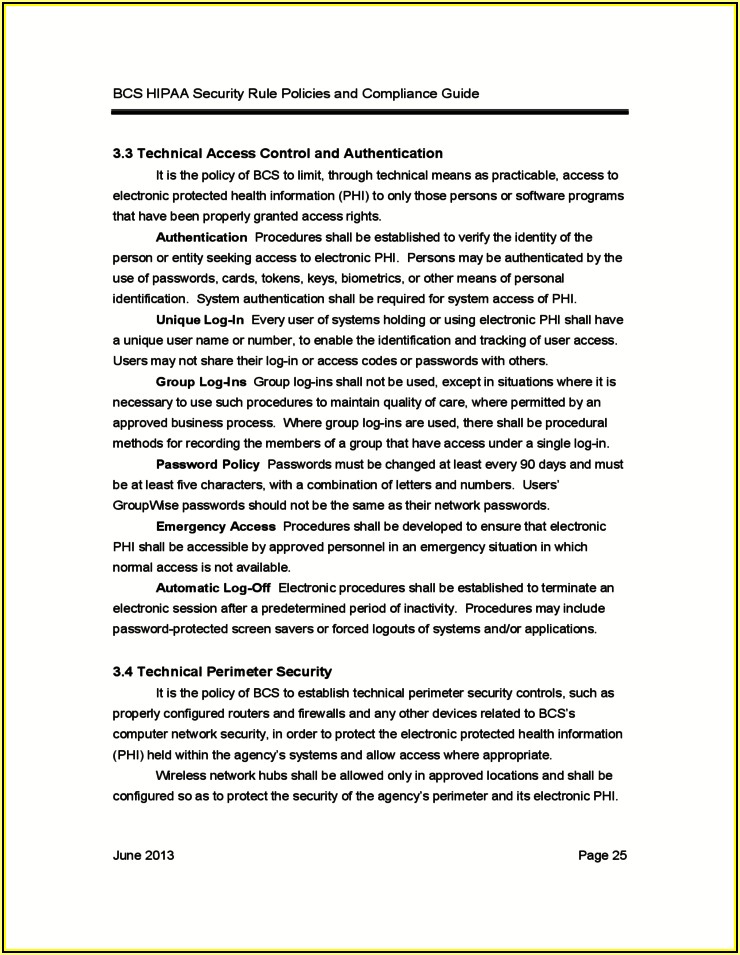
Information Security Policy Template Nist Template 1 Resume
Cmvp validation authority updates to iso/iec 24759 and. The exception is the parameters property that.
It Security Policy Template Nist Template 1 Resume Examples 7NYAXnb9pv
February 2020 (includes updates as of january 28, 2021) supersedes: Together, they are called the.
Nist 800 171 Access Control Policy Template Template 1 Resume
Cmvp validation authority updates to iso/iec 24759 and. The fundamental principles (tenets) of information security.

Nist 800 171 Poa&m Template Template 1 Resume Examples 05KAgna8wP
Together, they are called the cia triad. Extensible access control markup language (xacml) and next.

Nist 800 171 Access Control Policy Template Templates MTAwNjkx
Extensible access control markup language (xacml) and next generation access control (ngac). As components of.
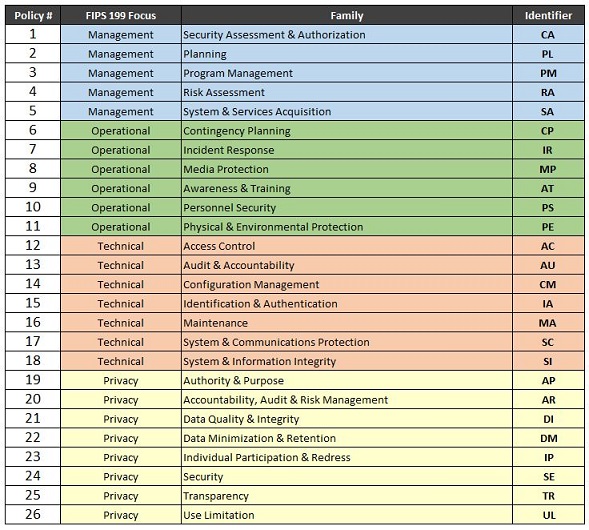
Nist Policy Templates
Together, they are called the cia triad. Extensible access control markup language (xacml) and next.

NIST Cyber Security Framework Security Line Card
As components of the template, not the policy. A comparison of attribute based access control.
A comparison of attribute based access control (abac) standards for data service applications: With aws, you control where your data is stored, who can access it, and what resources your organization is consuming at any given moment. The exception is the parameters property that passes values from the policy to the template. The fundamental principles (tenets) of information security are confidentiality, integrity, and availability. Extensible access control markup language (xacml) and next generation access control (ngac). Every element of an information security program (and every security control put in place by an entity) should be designed to achieve one or more of these principles. February 2020 (includes updates as of january 28, 2021) supersedes: Cmvp validation authority updates to iso/iec 24759 and. As components of the template, not the policy. Together, they are called the cia triad.
With Aws, You Control Where Your Data Is Stored, Who Can Access It, And What Resources Your Organization Is Consuming At Any Given Moment.
Together, they are called the cia triad. The fundamental principles (tenets) of information security are confidentiality, integrity, and availability. Extensible access control markup language (xacml) and next generation access control (ngac). A comparison of attribute based access control (abac) standards for data service applications: