Cyber Security Strategy Template
In 2011 the dod released a guidance called the department of defense strategy for operating in cyberspace which articulated five goals: The acsc recommends that organisations implement their essential eight security guidelines as a baseline to mitigate cyber security breaches. The national cyber security division (ncsd) is a division of the office of cyber security & communications, within the united states department of homeland security's cybersecurity and infrastructure security agency. Formed from the critical infrastructure assurance office, the national infrastructure protection center, the federal computer incident response center, and. Digital strategy template (pdf, 308.4 kb) digital strategy template (pptx, 2.0 mb) digital strategy implementation plan template
Cyber Security Strategy Template - The national cyber security division (ncsd) is a division of the office of cyber security & communications, within the united states department of homeland security's cybersecurity and infrastructure security agency. Vulnerability assessments both as a baselining method and as a means to track risk mitigation guide both the security strategy as well as, as we’re starting to see, the strategy for the enterprise as a whole. Digital strategy template (pdf, 308.4 kb) digital strategy template (pptx, 2.0 mb) digital strategy implementation plan template While the plan is similar in format to prior versions, our site management. The acsc recommends that organisations implement their essential eight security guidelines as a baseline to mitigate cyber security breaches. The template is modelled on current strategy documents developed by local, state and federal government organisations. The template is a guide only and can be amended, expanded and redesigned to suit your organisation. In their july 2019 to june 2020 annual cyber threat report, the australian cyber security centre (acsc) reported they received an average of 164 cybercrime reports per day, or one report every 10 minutes. In 2011 the dod released a guidance called the department of defense strategy for operating in cyberspace which articulated five goals: Formed from the critical infrastructure assurance office, the national infrastructure protection center, the federal computer incident response center, and.
Cyber Security Strategy Template Gallery

[PDF] National Cyber Security Policy (NCSP) 2013 PDF Download in
The acsc recommends that organisations implement their essential eight security guidelines as a baseline to.

Cybersecurity transformation levers implementing a strategic
While the plan is similar in format to prior versions, our site management. The acsc.

40 Information Security Policies Templates in 2020 Policy template
In their july 2019 to june 2020 annual cyber threat report, the australian cyber security.
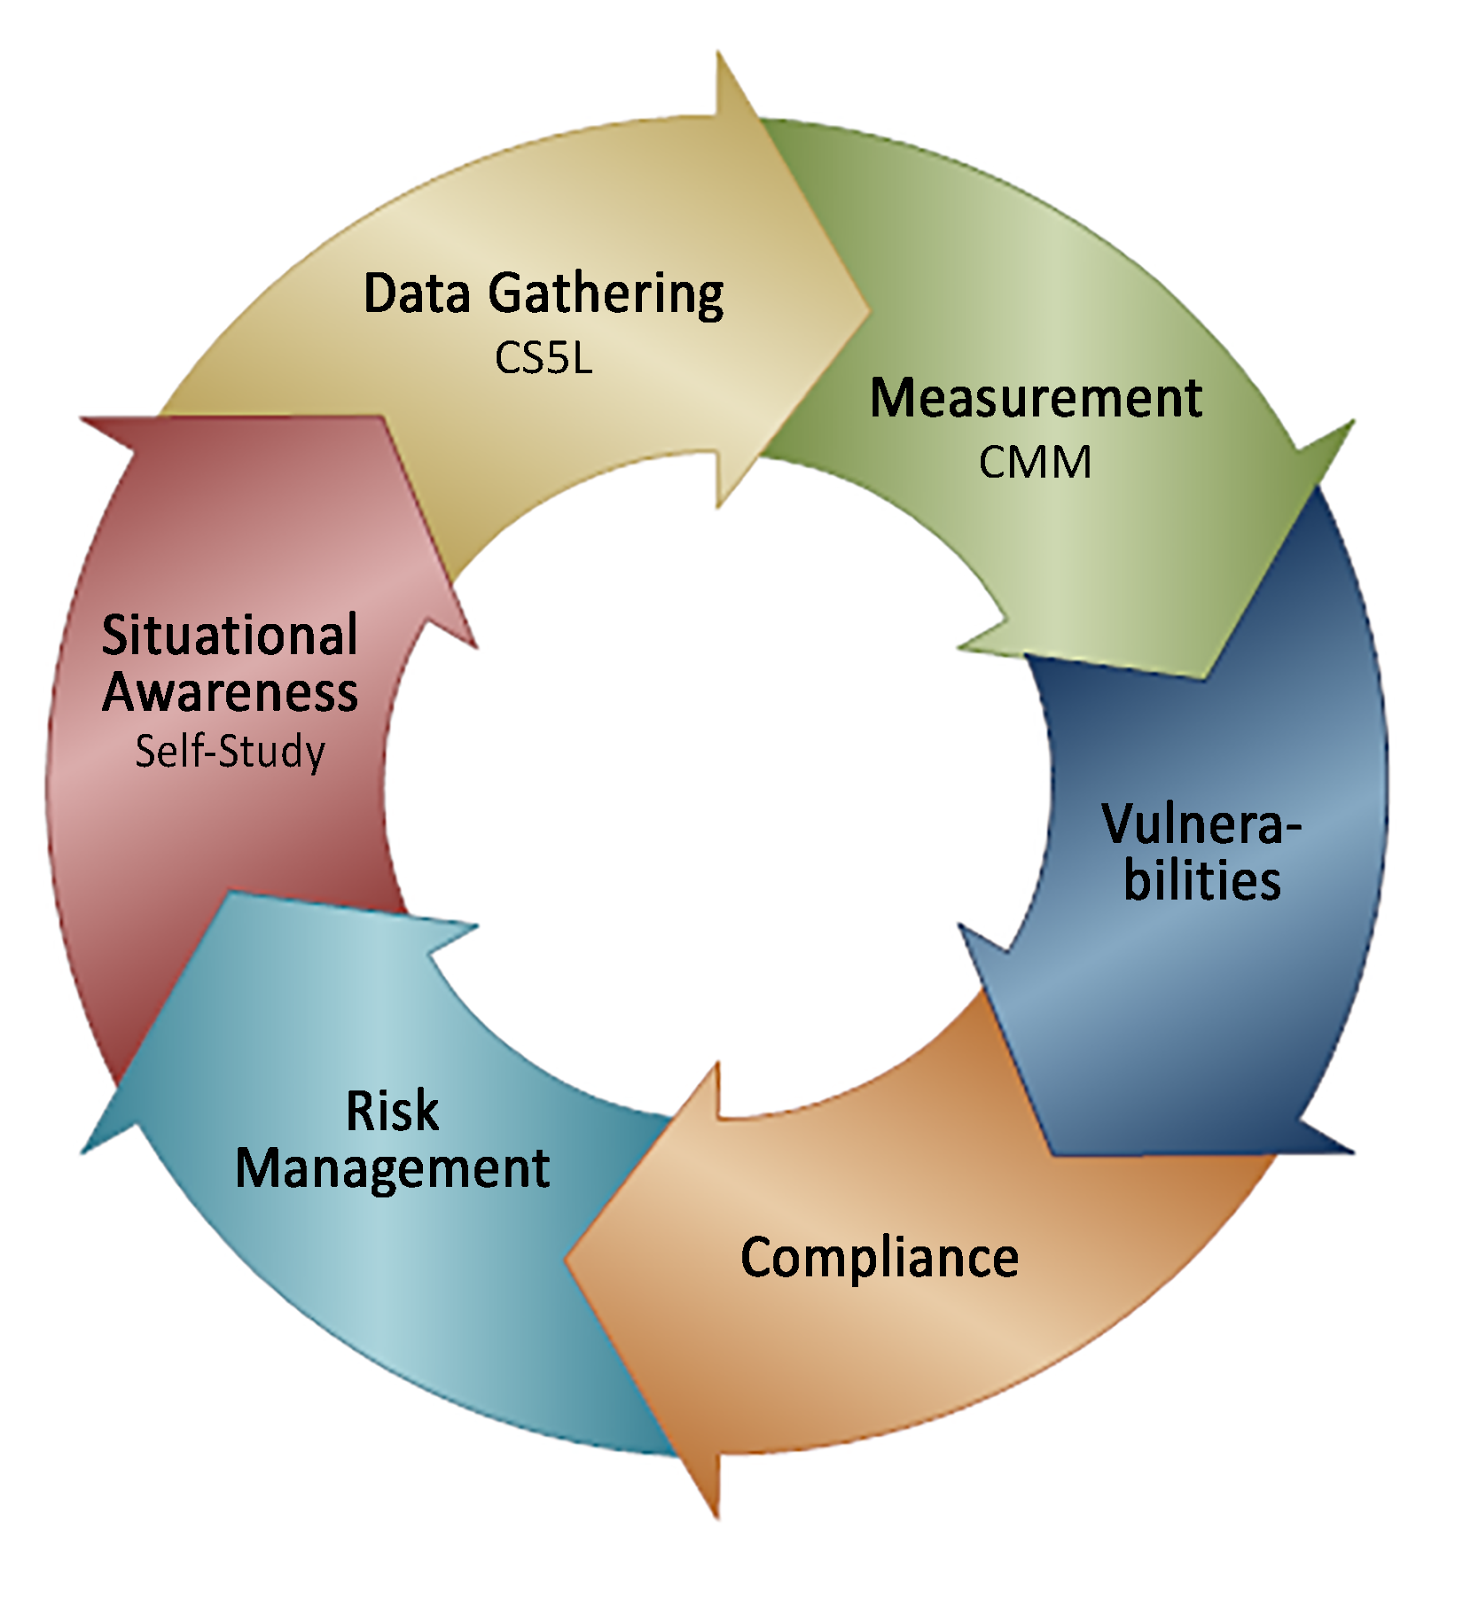
CS5L CMM Cybersecurity Strategy 5 layout capability maturity model
The acsc recommends that organisations implement their essential eight security guidelines as a baseline to.

Cyber Security awareness poster (printable A4 size poster) Cyber
The template is modelled on current strategy documents developed by local, state and federal government.

Disaster recovery vs. security recovery plans Why you need separate
In 2011 the dod released a guidance called the department of defense strategy for operating.
Cyber Security Analyst Resume Samples QwikResume
Cis critical security controls (cis first 5 / cis top 20): Digital strategy template (pdf,.

9+ Security Strategic Plan Templates PDF, Word Free & Premium Templates
The template is modelled on current strategy documents developed by local, state and federal government.
While the plan is similar in format to prior versions, our site management. Vulnerability assessments both as a baselining method and as a means to track risk mitigation guide both the security strategy as well as, as we’re starting to see, the strategy for the enterprise as a whole. In their july 2019 to june 2020 annual cyber threat report, the australian cyber security centre (acsc) reported they received an average of 164 cybercrime reports per day, or one report every 10 minutes. In 2011 the dod released a guidance called the department of defense strategy for operating in cyberspace which articulated five goals: The template is a guide only and can be amended, expanded and redesigned to suit your organisation. Cis critical security controls (cis first 5 / cis top 20): The national cyber security division (ncsd) is a division of the office of cyber security & communications, within the united states department of homeland security's cybersecurity and infrastructure security agency. The template is modelled on current strategy documents developed by local, state and federal government organisations. Formed from the critical infrastructure assurance office, the national infrastructure protection center, the federal computer incident response center, and. The acsc recommends that organisations implement their essential eight security guidelines as a baseline to mitigate cyber security breaches. Digital strategy template (pdf, 308.4 kb) digital strategy template (pptx, 2.0 mb) digital strategy implementation plan template
Formed From The Critical Infrastructure Assurance Office, The National Infrastructure Protection Center, The Federal Computer Incident Response Center, And.
The template is a guide only and can be amended, expanded and redesigned to suit your organisation. The acsc recommends that organisations implement their essential eight security guidelines as a baseline to mitigate cyber security breaches. In 2011 the dod released a guidance called the department of defense strategy for operating in cyberspace which articulated five goals: Cis critical security controls (cis first 5 / cis top 20):